Raffles Place is Singapore’s leading financial and business district, with banks, fintech companies, technology firms, professional-services organizations and regional headquarters operating in and around the area. As businesses increasingly rely on cloud platforms and digital services, demonstrating effective security and data-protection controls has become an important customer and business requirement.
Singapore’s digital economy reached S$128.1 billion in 2024, equivalent to 18.6% of GDP, according to IMDA. Finance and insurance remained a major contributor to Singapore’s digital economy, highlighting the importance of strong technology and information-security controls for businesses serving this market.
SOC 2 Type 2 in Raffles Place can help organizations demonstrate that relevant controls are suitably designed and have operated effectively over a defined period.
What Is SOC 2 Type 2 Certification?
SOC 2 is an AICPA reporting framework used to examine controls relevant to the Trust Services Criteria:
- Security
- Availability
- Processing Integrity
- Confidentiality
- Privacy
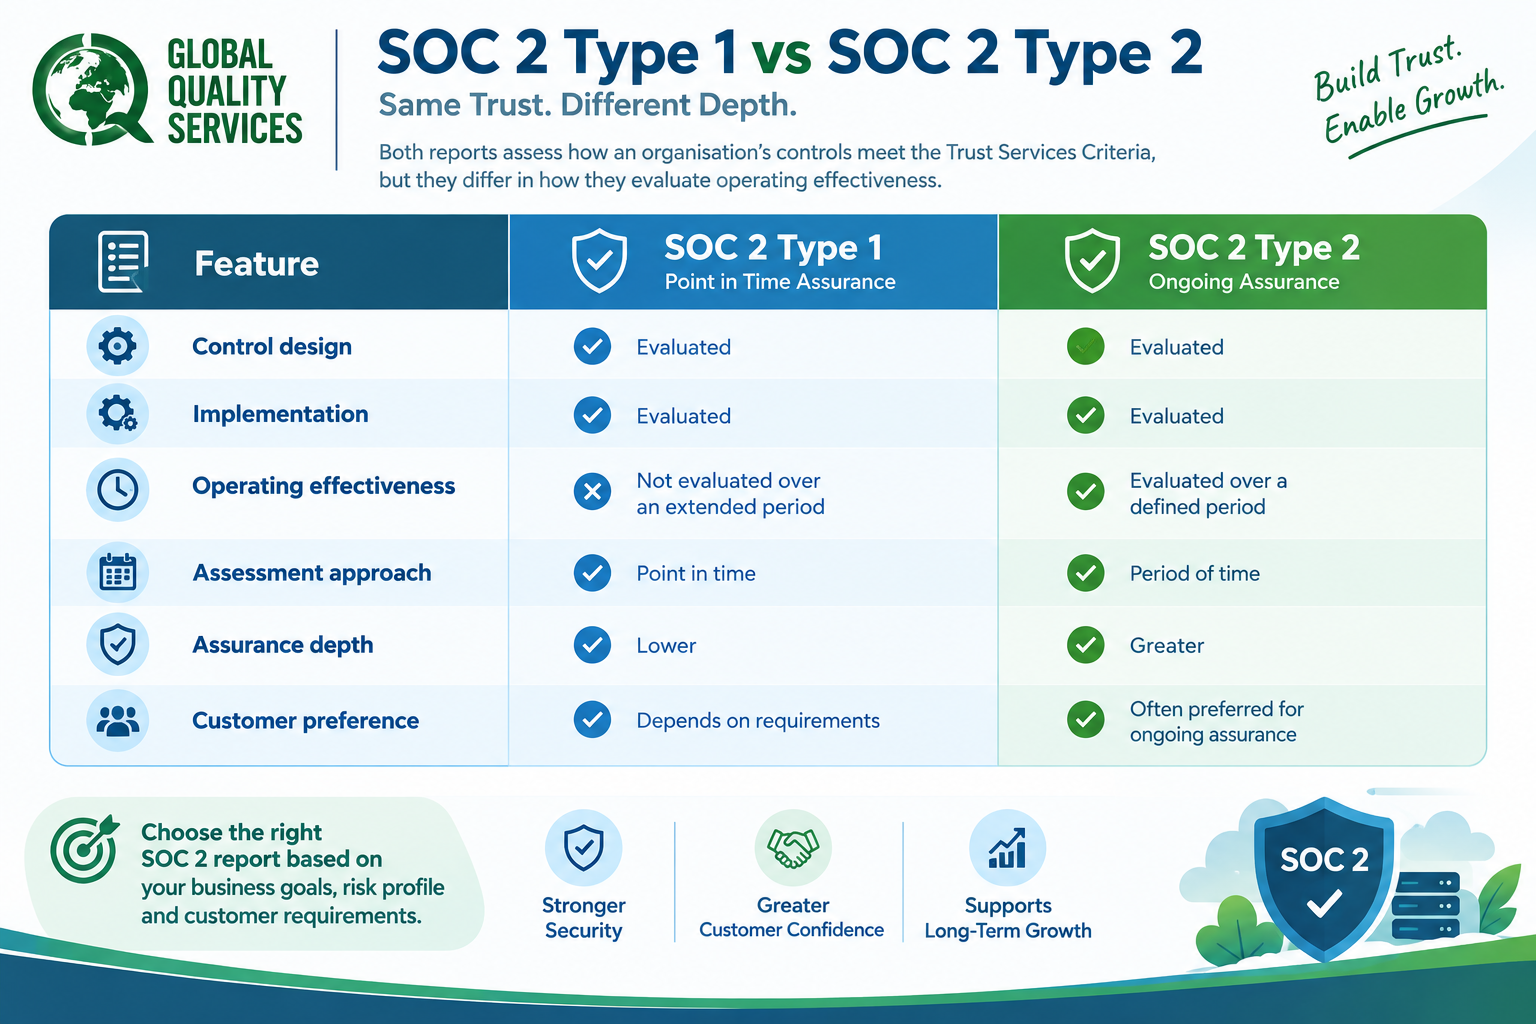
Organizations select the criteria relevant to their services, risks, and customer commitments. A Type 2 examination evaluates not only whether relevant controls are suitably designed, but also whether they operated effectively over a defined period.
This makes Type 2 particularly useful for enterprise customers that want evidence of ongoing control effectiveness rather than a point-in-time assessment.
SOC 2 Type 2 and Singapore Compliance Requirements
SOC 2 should not be treated as a substitute for Singapore’s laws or sector-specific regulatory requirements. However, the control framework can help organizations strengthen their broader governance and assurance environment.
Personal Data Protection Act
Singapore’s Personal Data Protection Act (PDPA) establishes requirements governing the collection, use, disclosure, and protection of personal data.
SOC 2 does not automatically demonstrate PDPA compliance. Organizations should separately assess their legal obligations under the PDPA while using relevant SOC 2 controls to strengthen their information-security and data-protection practices.
MAS Technology and Outsourcing Requirements
For businesses serving Singapore’s financial sector, MAS requirements on technology risk management, cyber hygiene, operational resilience, and outsourcing may also apply.
A SOC 2 report can provide useful independent assurance for customer and vendor due diligence, but it does not replace applicable MAS notices or guidelines.
Cybersecurity Act
Singapore’s Cybersecurity Act establishes a national cybersecurity framework, including requirements relating to Critical Information Infrastructure and specified cybersecurity services.
Organizations should determine whether the Act applies to their activities rather than treating SOC 2 as evidence of statutory compliance.
SOC 2 Type 2 Readiness Checklist
Before starting a SOC 2 Type 2 examination, an organization should first determine whether its systems, processes and controls are ready to be assessed over a defined period. A readiness review helps identify gaps before the independent examination begins and gives the organization time to address weaknesses.
Define the Scope and Trust Services Criteria
Start by clearly defining the services, applications, infrastructure, databases and business processes that will be included in the SOC 2 examination. The organization should also determine which Trust Services Criteria apply to its operations, such as Security, Availability, Processing Integrity, Confidentiality or Privacy.
The scope should reflect the services customers actually use and the commitments the organization makes to them.
Review Security and Access Controls
Access management is an important part of SOC 2 readiness. Organizations should review how users are created, approved, modified and removed, particularly for privileged and administrative accounts.
Multi-factor authentication, periodic access reviews, role-based permissions and employee offboarding should be supported by documented procedures and evidence showing that these controls are consistently followed.
Check Risk, Incident and Change Management
A SOC 2 readiness assessment should also examine how the organization identifies and manages security risks. This includes reviewing risk assessments, vulnerability management and corrective actions.
Incident-response procedures should be documented and tested where appropriate, while software and infrastructure changes should follow an established approval, testing and deployment process.
Review Vendors and Third Parties
Organizations should identify third parties that can affect the security or operation of systems within the SOC 2 scope. Vendor due diligence, contractual security requirements and periodic reviews should be appropriate to the risks associated with each supplier.
Where important services are provided by subservice organizations, their controls and relevant assurance reports should also be considered during the readiness process.
Prepare for Evidence Collection
One of the most important aspects of Type 2 readiness is evidence. It is not enough to have policies and controls documented. The organization needs to demonstrate that relevant controls actually operated during the examination period.
Evidence may include access reviews, change approvals, security-monitoring records, vulnerability assessments, incident records, employee training records, vendor assessments and backup or recovery testing.
Review Business Continuity and Data Protection
Organizations should review backup, disaster-recovery and business-continuity arrangements where Availability is within scope. Data protection should also be assessed, particularly where the organization handles confidential or personal information.
For businesses operating in Singapore, this review should also consider applicable obligations under the Personal Data Protection Act (PDPA) and any sector-specific requirements relevant to the organization.
Conduct a Final Readiness Review
Before the independent SOC 2 Type 2 examination, management should confirm that controls have assigned owners, required evidence is available, identified exceptions have been addressed and employees understand their responsibilities.
A readiness assessment can help organizations identify gaps early rather than discovering them during the formal examination.
How is SOC 2 Type 2 Certification Different from SOC2 Type 1?
Who Should Consider SOC 2 Type 2 in Raffles Place?
SOC 2 Type 2 certification is particularly relevant to businesses that provide technology-enabled services or handle customer information.
Fintech and Financial Technology Companies
Fintech businesses serving banks, financial institutions, and enterprise customers may need to demonstrate strong security and operational controls.
SaaS and Cloud Service Providers
SaaS companies and cloud-based service providers can use SOC 2 reporting to address customer security reviews and enterprise procurement requirements.
Technology and Software Companies
Software developers and technology companies handling customer systems, applications,ons or business data can use SOC 2 to strengthen their security assurance.
Data and Analytics Companies
Organizations processing, analyzing, or storing customer or business data may benefit from controls covering security, confidentiality, privacy,y, and processing integrity.
Payment Technology Providers
Payment technology businesses may face increased expectations around security, availability, data protection and operational resilience.
Professional and Business Services
Service providers that host, process, or manage customer information through digital systems can also evaluate whether SOC 2 fits their business.
Benefits of SOC 2 Type 2 for Raffles Place Businesses
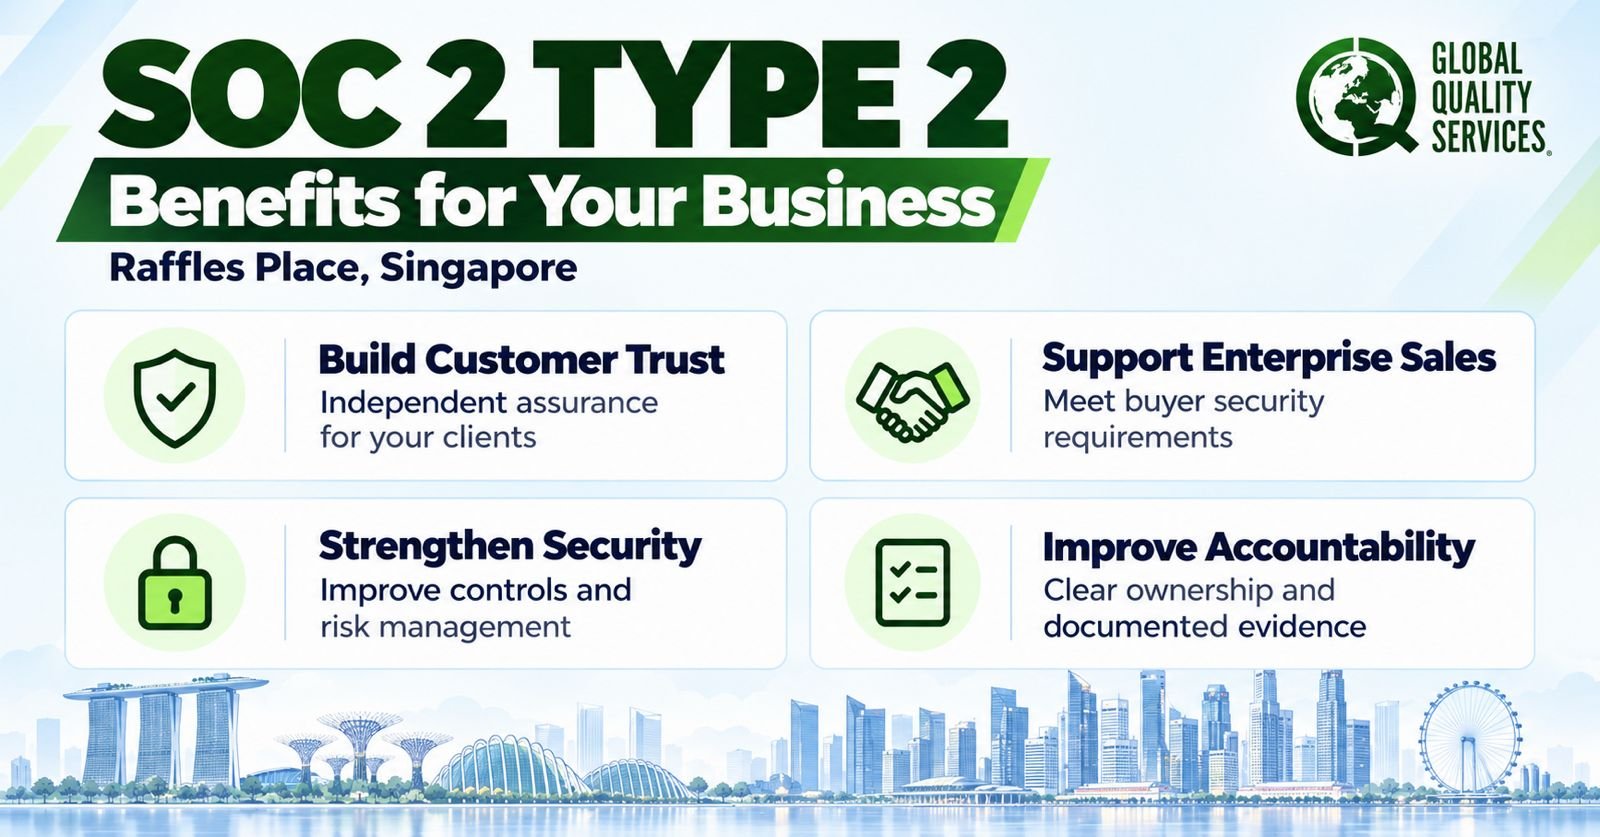
Demonstrates Ongoing Control Effectiveness
Type 2 provides evidence that relevant controls operated effectively throughout the examination period.
Supports Enterprise Customer Requirements
Large customers may request independent assurance before onboarding technology and service providers.
Strengthens Vendor Due Diligence
A SOC 2 report gives customers structured information when evaluating a service provider’s security and operational controls.
Improves Internal Security Governance
Preparing for SOC 2 can identify weaknesses in access management, monitoring, change management, incident response, and vendor management.
Supports Business Expansion
For Singapore companies serving customers across Asia-Pacific, SOC 2 can provide a recognized form of independent assurance that supports international business discussions.
What Does SOC 2 Type 2 Cover?
The scope of a SOC 2 examination depends on the organization’s services and the Trust Services Criteria selected.
Security Controls
Security is the foundation of SOC 2 and may include:
- Identity and access management
- Multi-factor authentication
- Privileged access management
- Security monitoring
- Vulnerability management
- Incident response
- Risk assessment
- Change management
- Logical and physical security
Availability Controls
Where availability is included, controls may address system monitoring, backup, disaster recovery, capacity management, business continuity and recovery procedures.
Processing Integrity Controls
These controls address whether system processing is complete, valid, accurate, timely,y and authorized according to defined requirements.
Confidentiality Controls
Confidentiality controls protect information identified as confidential from unauthorized access, disclosure, or use.
Privacy Controls
Privacy is included; controls address the organization’s practices for collecting, using, retaining, disclosing, and disposing of personal information.
SOC 2 Type 2 Certification Process in Raffles Place
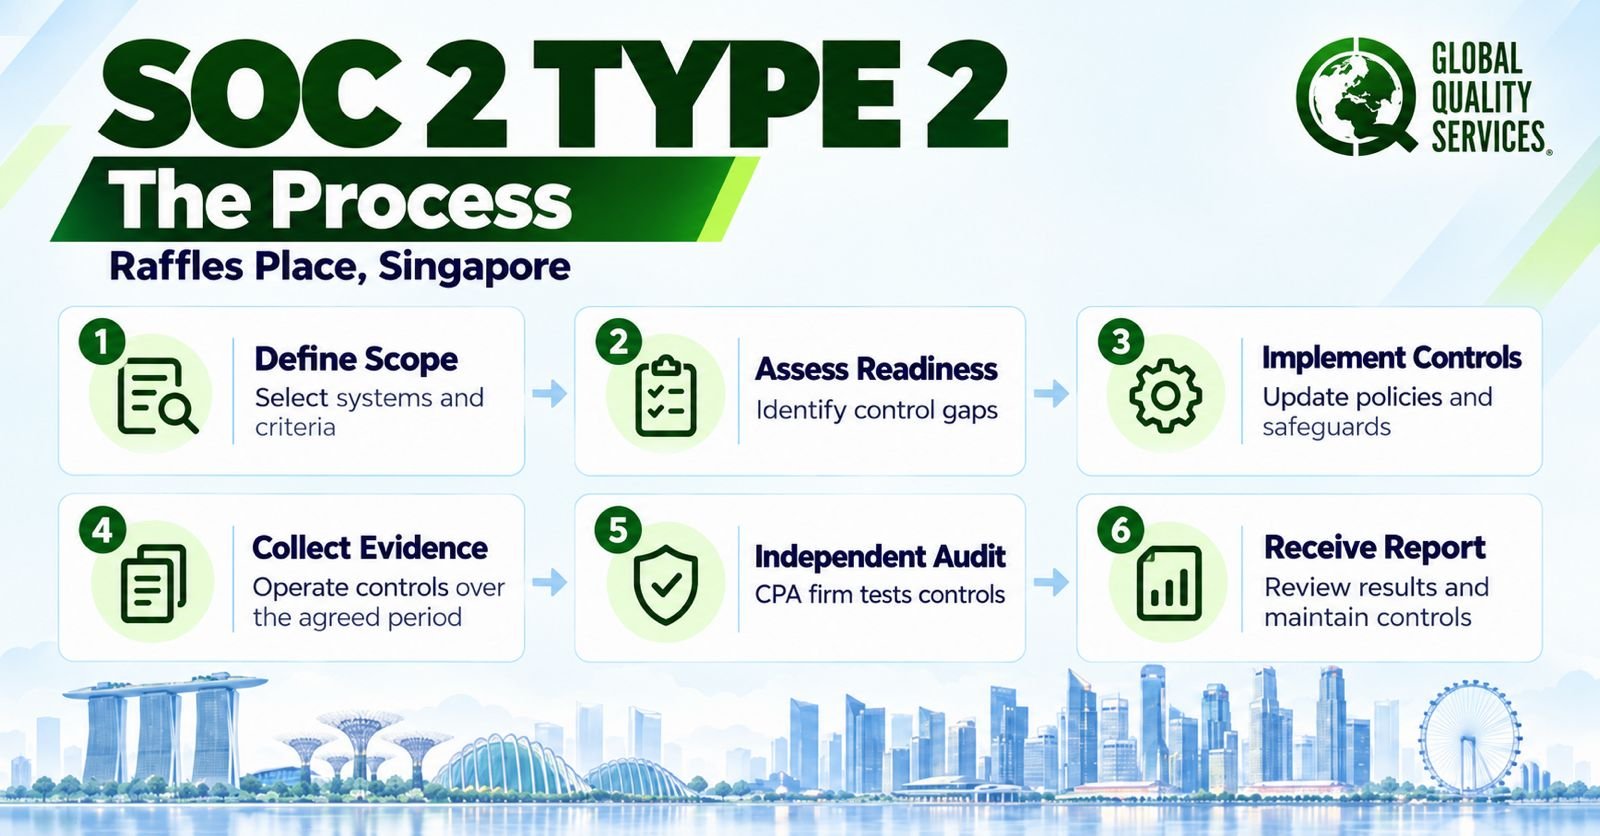
1. Define the Scope
Identify the services, applications, infrastructure, systems, locations,s and business processes included in the examination.
2. Select the Trust Services Criteria
Determine which criteria apply based on customer commitments, business activities, es and risk.
3. Conduct a Gap Assessment
Review existing controls against the selected SOC 2 requirements and identify weaknesses to address.
4. Implement Controls
Develop or strengthen controls covering access management, security monitoring, change management, incident response, vendor management, business continuity, and data protection.
5. Establish Evidence Collection
Create consistent processes to collect and retain evidence that controls operate as required.
6. Conduct Employee Awareness
Ensure employees understand relevant security policies, procedures, and control responsibilities.
7. Perform a Readiness Review
Review the control environment and available evidence before the independent examination.
8. Complete the Type 2 Examination
The independent service auditor evaluates the design and operating effectiveness of relevant controls over the defined examination period.
9. Receive the SOC 2 Report
After completing the examination, the independent service auditor issues the applicable SOC 2 Type 2 report.
Why Choose GQS for SOC 2 Type 2 Readiness?
Global Quality Services provides consultancy and compliance-readiness support to organizations operating in Singapore.
For SOC 2 projects, GQS focuses on practical control preparation and examination readiness. The qualified independent service auditor remains responsible for the independent SOC 2 examination.
This separation helps preserve the independence required for the final attestation report.
Frequently Asked Questions
Is SOC 2 Type 2 mandatory in Singapore?
No. SOC 2 Type 2 is not a general legal requirement for Singapore businesses. However, customers, enterprise buyers, or business partners may require it as part of their vendor due diligence.
Is SOC 2 Type 2 a certification?
No. SOC 2 Type 2 is an independent attestation report, not an ISO-style certification.
Does SOC 2 Type 2 prove PDPA compliance?
No. SOC 2 and the PDPA serve different purposes. A SOC 2 report can assure relevant controls but does not automatically demonstrate compliance with every PDPA obligation.
How long does SOC 2 Type 2 take?
The timeline depends on the organization’s scope, existing control maturity, and selected Trust Services Criteria. Type 2 also requires evidence that controls operated effectively over a defined examination period.
Can SaaS companies in Raffles Place obtain SOC 2 Type 2?
Yes. SaaS and technology companies commonly use SOC 2 reporting to demonstrate security and control effectiveness to enterprise customers.
Who issues the SOC 2 Type 2 report?
An independent qualified service auditor or CPA firm performs the examination and issues the report. A consultancy providing readiness support does not issue the independent attestation report.