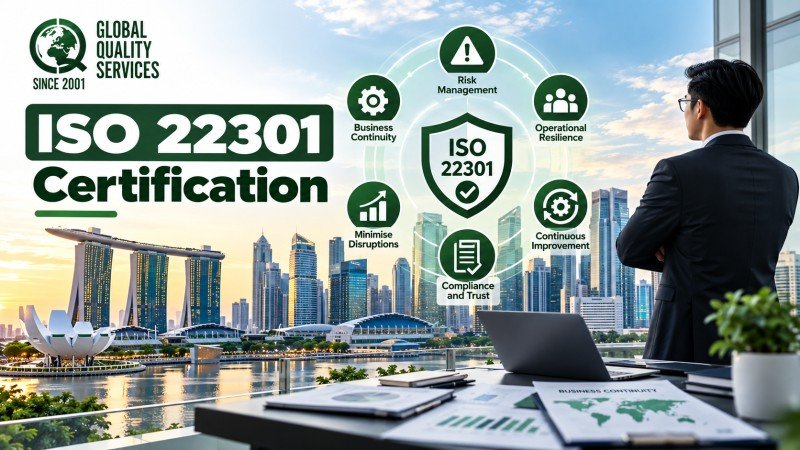
ISO 22301:2019 is the international standard for business continuity management, specifying requirements for planning, establishing, implementing, operating, monitoring, reviewing, maintaining, and continually improving a BCMS. It replaces BS 25999 and focuses on protecting critical operations during and after disruptions, ensuring quick recovery to minimize downtime and financial losses.
Unlike general ISO standards, ISO 22301 certification in Singapore emphasizes risk-based thinking, business impact analysis (BIA), and recovery strategies aligned with organizational context. It applies to all sizes, from SMEs to multinationals, and integrates seamlessly with ISO 27001 (information security), ISO 9001 (quality), and ISO 14001 (environment).
In Singapore’s high-stakes economy, regulated by the Monetary Authority of Singapore (MAS) and Infocomm Media Development Authority (IMDA), ISO 22301 demonstrates regulatory alignment and crisis readiness.
What is ISO 22301 Certification
ISO 22301 certification confirms that an organisation has established a Business Continuity Management System (BCMS) to prepare for, respond to, and recover from disruptions. It helps businesses identify critical operations, assess potential risks, develop continuity plans, and maintain essential services during unexpected events, such as cyberattacks, equipment failures, or natural disasters.
Why Does ISO 22301 Certification Matter
ISO 22301 matters because business disruptions can affect revenue, customer trust, and daily operations. It helps your team prepare for unexpected events, respond with clear responsibilities, and restore critical services faster. Certification also demonstrates your commitment to business continuity, which can strengthen confidence among customers, suppliers, and business partners.
Key Requirements for ISO 22301 Certification
Achieving ISO 22301 certification involves 10 clauses under the High-Level Structure (HLS):
- Context of the Organization: Understand internal/external issues, stakeholder needs, and BCMS scope.
- Leadership: Top management commitment, policy, and roles.
- Planning: Risk assessment, BIA, recovery time objectives (RTOs), recovery point objectives (RPOs).
- Support: Resources, competence, awareness, communication, documented information.
- Operation: Business continuity plans (BCPs), incident response, testing/exercises.
- Performance Evaluation: Monitoring, internal audits, management reviews.
- Improvement: Nonconformity handling, continual enhancement.
Global Quality Services conducts an ISO 22301 gap analysis to map your current state, prioritizing high-impact areas like supply chain vulnerabilities common in Singapore’s trade-dependent market.
Step-by-Step ISO 22301 Certification Process in Singapore
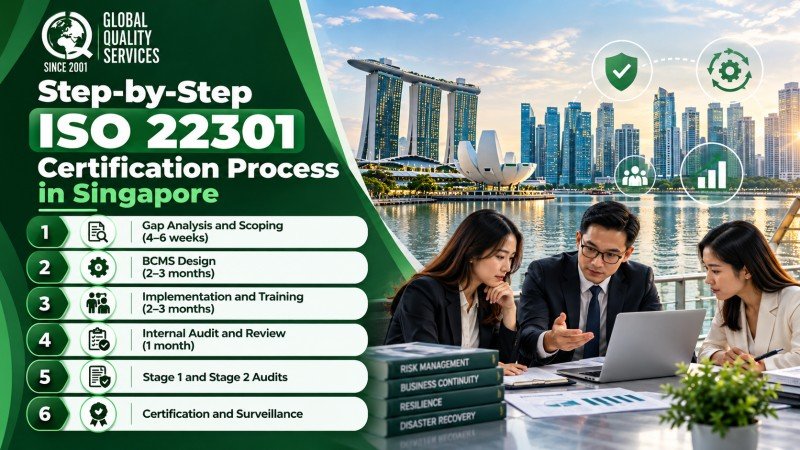
Our proven ISO 22301 implementation roadmap ensures certification in 6-12 months:
Step 1: Gap Analysis and Scoping (4–6 weeks)
Assess your current business continuity practices against ISO 22301 requirements. Conduct a Business Impact Analysis (BIA) to identify critical activities, dependencies, recovery priorities, and the scope of your Business Continuity Management System (BCMS).
Step 2: BCMS Design (2–3 months)
Develop your BCMS using the findings from the gap analysis and BIA. Establish continuity policies, assess business disruption risks, create a risk register, and prepare Business Continuity Plans (BCPs) for critical operations.
Step 3: Implementation and Training (2–3 months)
Implement the approved continuity procedures across relevant departments. Train employees on their responsibilities, communicate recovery arrangements, and conduct drills or simulations to evaluate whether teams can respond effectively to business disruptions.
Step 4: Internal Audit and Review (1 month)
Conduct an internal audit to check whether your BCMS meets ISO 22301 requirements. Review continuity plans, test records, and recovery procedures, then address gaps before the external certification audit.
Step 5: Stage 1 and Stage 2 Audits
Engage a certification body accredited for ISO 22301. During Stage 1, auditors review documentation and readiness. During Stage 2, they evaluate implementation, interview staff, and test the BCMS’s effectiveness.
Step 6: Certification and Surveillance
After meeting certification requirements and resolving relevant nonconformities, your organisation can receive ISO 22301 certification. The certification cycle generally lasts three years, with periodic surveillance audits to assess ongoing compliance.
Benefits of ISO 22301 Certification in Singapore
ISO 22301 benefits are transformative:
| Benefit | Impact | Singapore Relevance |
|---|---|---|
| Resilience | 85% report fewer disruptions, 60% faster recovery | Critical for typhoons and cyber threats under the Cybersecurity Act |
| Cost Savings | 28% lower insurance premiums, minimized downtime losses | Supports SME survival amid rising costs |
| Competitive Edge | Wins tenders (52% improved customer satisfaction) | MAS/IMDA procurement mandates |
| Risk Management | Streamlined BIA/RTOs, 74% better analytics | Aligns with PDPA, supply chain regs |
| Stakeholder Trust | Global recognition, employee buy-in (40% higher) | Boosts ASEAN exports, investor confidence |
| Compliance | Meets legal requirements, reduces fines | Essential for fintech, logistics hubs |
85% of certified firms note enhanced resilience per industry scans.
Why Choose Global Quality Services for ISO 22301 in Singapore?
With 26+ years as an ISO 27001-certified consultancy in Jurong East and Tampines, Global Quality Services excels in ISO 22301 consulting services in Singapore. We serve 500+ clients across Asia, offering bundled ISO 22301 training, BCP software integration, and post-certification maintenance. Our SAC-accredited partnerships ensure unbiased audits. Tailored for Singapore SMEs and MNCs, we address local risks like port disruptions or data sovereignty.
Post-certification, conduct annual internal audits, management reviews, and exercises (e.g., tabletop simulations). Recertify every 3 years. GQS provides subscription audits, updating for ISO revisions and emerging threats like AI-driven risks.
Frequently Asked Questions
1. How often should a company test its business continuity plan after ISO 22301 certification?
Companies should test their business continuity plans at planned intervals and after significant operational changes. Regular exercises help teams identify weaknesses and improve their response.
2. Can a small business apply for ISO 22301 certification without a dedicated risk management team?
Yes, small businesses can pursue certification by assigning continuity responsibilities to existing employees. They can develop practical procedures based on their operations, resources, and business risks.
3. What records should a company maintain to prepare for an ISO 22301 surveillance audit?
Companies should maintain risk assessments, business impact analyses, recovery plans, training records, exercise results, incident reports, corrective actions, and management review records for auditor verification.
4. What happens if a company fails to meet an ISO 22301 audit requirement?
The auditor may raise a nonconformity that requires investigation and corrective action. The company must address the finding within the applicable certification body’s specified timeframe.
5. Does ISO 22301 certification need an update when a company opens a new branch?
Yes, companies should review their business continuity plans when opening new branches. They must assess location-specific risks, critical processes, recovery arrangements, and resource requirements.